EMT Practice Test

1. Question Content...


Question List

Question1: What integration allows searching and displaying Splunk results within Cortex XSOAR?

Question2: What does DBot use to score an indicator that has multiple reputation scores?

Question3: Which two log types should be configured for firewall forwarding to the Cortex Data Lake for use by Cortex XDR? (Choose two)

Question4: What are two ways a customer can configure user authentication access Cortex Xpanse?
(Choose two.)

Question5: What does Cortex Xpanse ingest from XDR endpoints?

Question6: Which Cortex XDR license is required for a customer that requests endpoint detection and response (EDR) data collection capabilities?

Question7: What is the primary mechanism for the attribution of attack surface data in Cortex Xpanse?

Question8: How does a clear understanding of a customer's technical expertise assist in a hand off following the close of an opportunity?

Question9: What are two manual actions allowed on War Room entries? (Choose two.)

Question10: How does the integration between Cortex Xpanse and Cortex XSOAR benefit security teams?

Question11: What is the retention requirement for Cortex Data Lake sizing?

Question12: What is a benefit of user entity behavior analytics (UEBA) over security information and event management (SIEM)?

Question13: Which playbook functionality allows grouping of tasks to create functional building blocks?

Question14: Which two filter operators are available in Cortex XDR? (Choose two.)

Question15: Which product enables the discovery, exchange, and contribution of security automation playbooks, built into Cortex XSOAR?

Question16: Where is the best place to find official resource material?

Question17: Which description applies to the features of the Cortex platform as a holistic ecosystem?

Question18: Cortex XDR external data ingestion processes ingest data from which sources?

Question19: Which step is required to prepare the virtual desktop infrastructure (VDI) golden image?

Question20: How does an "inline" auto-extract task affect playbook execution?

Question21: A Cortex XSOAR customer wants to ingest from a single mailbox. The mailbox brings in reported phishing emails and email requests from human resources (HR) to onboard new users. The customer wants to run two separate workflows from this mailbox, one for phishing and one for onboarding. What will allow Cortex XSOAR to accomplish this in the most efficient way?

Question22: For which two purposes can Cortex XSOAR engines be deployed? (Choose two.)

Question23: In the DBotScore context field, which context key would differentiate between multiple entries for the same indicator in a multi-TIP environment?

Question24: An antivirus refresh project was initiated by the IT operations executive. Who is the best source for discussion about the project's operational considerations?

Question25: Which statement applies to a Cortex XSOAR engine that is part of a load-balancing group?

Question26: A customer has 2700 endpoints. There is currently concern about recent attacks in their industry and threat intelligence from a third-party subscription. In an attempt to be proactive, phishing simulations have been prioritized, but the customer wants to gain more visibility and remediation capabilities specific to their network traffic.
Which Cortex product provides these capabilities?

Question27: Given the exception thrown in the accompanying image by the Demisto REST API integration, which action would most likely solve the problem?

Which two playbook functionalities allow looping through a group of tasks during playbook execution? (Choose two.)

Question28: Which action allows Cortex XSOAR to access Docker in an air-gapped environment where the Docker page was manually installed after the Cortex XSOAR installation?

Question29: What is a requirement when integrating Cortex XSIAM or Cortex XDR with other Palo Alto Networks products?

Question30: A Cortex XSOAR customer has a phishing use case in which a playbook has been implemented with one of the steps blocking a malicious URL found in an email reported by one of the users.
What would be the appropriate next step in the playbook?

Question31: Which step is required to prepare the VDI Golden Image?

Question32: Which two entities can be created as a behavioral indicator of compromise (BIOC)? (Choose two.)

Question33: Which Cortex XDR capability prevents running malicious files from USB-connected removable equipment?

Question34: A customer has purchased Cortex XSOAR and has a need to rapidly stand up the product in their environment. The customer has stated that their internal staff are currently occupied with other projects.
Which Palo Alto Networks service offering should be recommended to the customer?

Question35: Which consideration should be taken into account before deploying Cortex XSOAR?

Question36: Which type of log is ingested natively in Cortex XDR Pro per TB?

Question37: Cortex XSOAR has extracted a malicious Internet Protocol (IP) address involved in command- and-control (C2) traffic.
What is the best method to block this IP from communicating with endpoints without requiring a configuration change on the firewall?

Question38: Which action should be performed by every Cortex Xpanse proof of value (POV)?

Question39: Which playbook feature allows concurrent execution of tasks?

Question40: When a Demisto Engine is part of a Load-Balancing group it?

Question41: Which Cortex XDR capability extends investigations to an endpoint?

Question42: Which Cortex XSIAM feature can be used to onboard data sources?

Question43: Which Cortex XDR Agent capability prevents loading malicious files from USB-connected removable equipment?

Question44: The customer has indicated they need EDR data collection capabilities, which Cortex XDR license is required?

Question45: What are process exceptions used for?

Question46: Why is it important to document notes from the Proof of Value (POV) for post-sales hand off?

Question47: A test for a Microsoft exploit has been planned. After some research Internet Explorer 11 CVE-
2016-0189 has been selected and a module in Metasploit has been identified (exploit/windows/browser/ms16_051_vbscript) The description and current configuration of the exploit are as follows:

What is the remaining configuration?

Question48: A prospect has agreed to do a 30-day POC and asked to integrate with a product that Demisto currently does not have an integration with. How should you respond?

Question49: What are two capabilities of a War Room? (Choose two.)

Question50: How does Cortex XSOAR automation save time when a phishing incident occurs?

Question51: Which command-line interface (CLI) query would retrieve the last three Splunk events?

Question52: Which service helps identify attackers by combining world-class threat intelligence with Cortex XSIAM technology?

Question53: Which statement best describes the benefits of the combination of Prisma Cloud, Cortex Xpanse, and partner services?

Question54: In Cortex XDR Prevent, which three matching criteria can be used to dynamically group endpoints? (Choose three.)

Question55: A prospective customer is interested in Cortex XDR but is enable to run a product evaluation.
Which tool can be used instead to showcase Cortex XDR?

Question56: Which attack method is a result of techniques designed to gain access through vulnerabilities in the code of an operating system (OS) or application?

Question57: Approximately how many Cortex XSOAR marketplace integrations exist?

Question58: What is the primary function of an engine in Cortex XSOAR?

Question59: An adversary attempts to communicate with malware running on a network in order to control malware activities or to exfiltrate data from the network.
Which Cortex XDR Analytics alert will this activity most likely trigger?

Question60: In Cortex XDR Prevent, which three matching criteria can be used to dynamically group endpoints? (Choose three )

Question61: A customer is hesitant to directly connect their network to the Cortex platform due to compliance restrictions.
Which deployment method should the customer use to ensure secure connectivity between their network and the Cortex platform?

Question62: Which two statements apply to widgets? (Choose two.)
Question63: Which two types of indicators of compromise (IOCs) are available for creation in Cortex XDR?
(Choose two.)

Question64: In addition to migration and go-live, what are two best-practice steps for migrating from SIEM to Cortex XSIAM? (Choose two.)

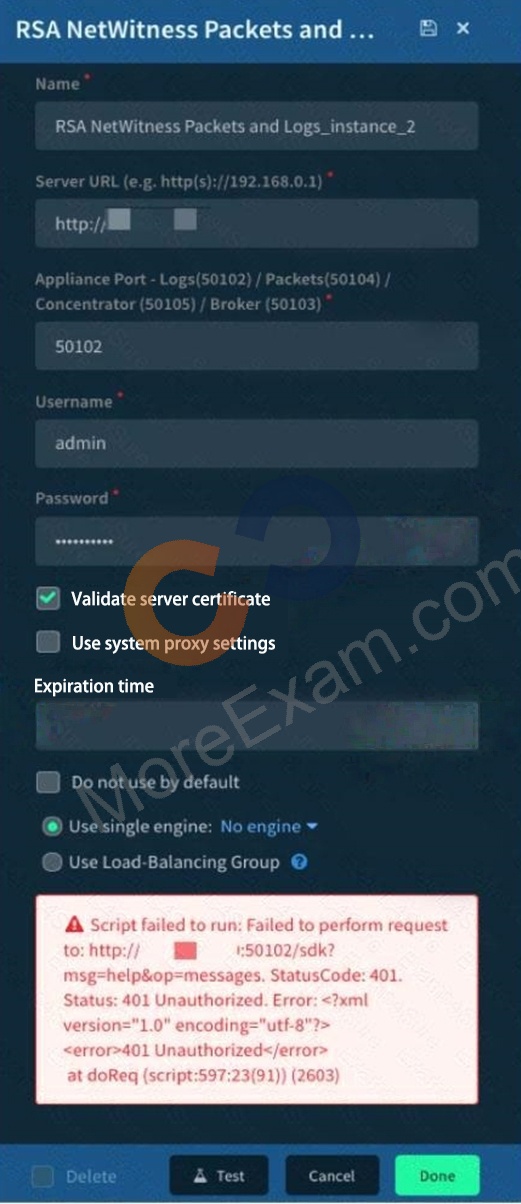
Question65: Given the integration configuration and error in the screenshot what is the cause of the problem?

Question66: Which Cortex XSIAM license is required if an organization needs to protect a cloud Kubernetes host?

Question67: The images show two versions of the same automation script and the results they produce when executed in Demisto.
What are two possible causes of the exception thrown in the second Image? (Choose two.)

Question68: Which two manual actions are allowed on War Room entries? (Choose two.)

Question69: Which task setting allows context output to a specific key?

Question70: An administrator of a Cortex XDR protected production environment would like to test its ability to protect users from a known flash player exploit.
What is the safest way to do it?

Question71: Which technology allows a customer to integrate Cortex Xpanse with third-party applications or services, assets, and IP ranges while leveraging investigation capabilities?

Question72: Which aspect of Cortex Xpanse allows for visibility over remote workforce risks?

Question73: Which two methods does the Cortex XDR agent use to identify malware during a scheduled scan? (Choose two.)

Question74: Which deployment type supports installation of an engine on Windows, Mac OS, and Linux?

Question75: An Administrator is alerted to a Suspicious Process Creation security event from multiple users.
The users believe that these events are false positives Which two steps should the administrator take to confirm the false positives and create an exception? (Choose two )

Question76: The Cortex XDR management service requires which other Palo Alto Networks product?

Question77: Which two formats are supported by Whitelist? (Choose two)

Question78: Which feature in Cortex XSIAM extends analytics detections to all mapped network and authentication data?

Question79: What must a customer deploy prior to collecting endpoint data in Cortex XSIAM?

Question80: A Cortex XSIAM customer is unable to access their Cortex XSIAM tenant.
Which resource can the customer use to validate the uptime of Cortex XSIAM?

Question81: Which two actions are required to add indicators to the whitelist? (Choose two.)

Question82: Within Cortex XSIAM, how does the integration of Attack Surface Management (ASM) provide a unified approach to security event management that traditional SIEMs typically lack?

Question83: Which option is required to prepare the VDI Golden Image?

Question84: When initiated, which Cortex XDR capability allows immediate termination of the process or whole process tree on an anomalous process discovered during investigation of a security event?

Question85: In addition to incident volume, which four critical factors must be evaluated to determine effectiveness and ROI on cybersecurity planning and technology?