EMT Practice Test

1. Question Content...


Question List

Question1: A customer wants to modify the retention periods of their Threat logs in Cortex Data Lake.
Where would the user configure the ratio of storage for each log type?

Question2: What are two manual actions allowed on War Room entries? (Choose two.)

Question3: If a customer activates a TMS tenant and has not purchased a Cortex Data Lake instance.
Palo Alto Networks will provide the customer with a free instance
What size is this free Cortex Data Lake instance?

Question4: In Cortex XDR Prevent, which three matching criteria can be used to dynamically group endpoints? (Choose three.)

Question5: Which four types of Traps logs are stored within Cortex Data Lake?

Question6: An EDR project was initiated by a CISO. Which resource will likely have the most heavy influence on the project?

Question7: Rearrange the steps into the correct order for modifying an incident layout.
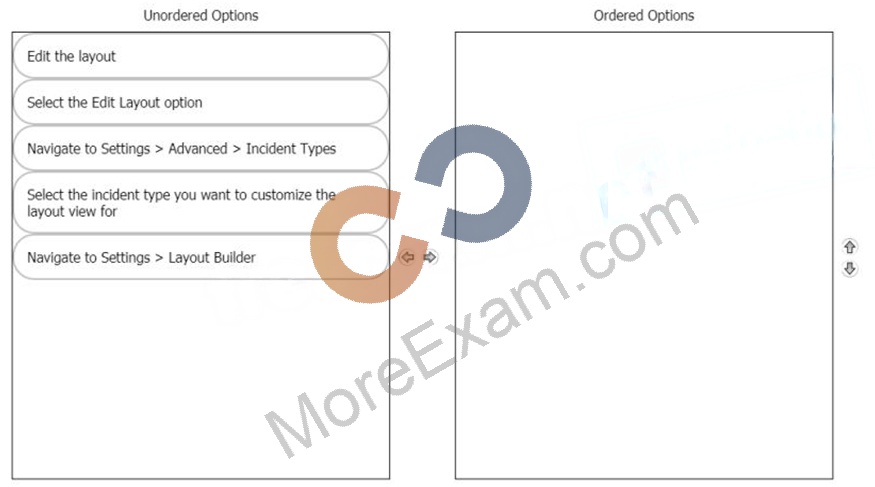
Question8: The customer has indicated they need EDR data collection capabilities, which Cortex XDR license is required?

Question9: A prospect has agreed to do a 30-day POC and asked to integrate with a product that Demisto currently does not have an integration with. How should you respond?

Question10: Which two formats are supported by Whitelist? (Choose two)

Question11: The certificate used for decryption was installed as a trusted root CA certificate to ensure communication between the Cortex XDR Agent and Cortex XDR Management Console What action needs to be taken if the administrator determines the Cortex XDR Agents are not communicating with the Cortex XDR Management Console?

Question12: If an anomalous process is discovered while investigating the cause of a security event, you can take immediate action to terminate the process or the whole process tree, and block processes from running by initiating which Cortex XDR capability?

Question13: Which option is required to prepare the VDI Golden Image?

Question14: The prospect is deciding whether to go with a phishing or a ServiceNow use case as part of their POC We have integrations for both but a playbook for phishing only Which use case should be used for the POC?

Question15: An adversary is attempting to communicate with malware running on your network for the purpose of controlling malware activities or for ex filtrating data from your network. Which Cortex XDR Analytics alert is this activity most likely to trigger'?

Question16: How many use cases should a POC success criteria document include?

Question17: Given the exception thrown in the accompanying image by the Demisto REST API integration, which action would most likely solve the problem?

Which two playbook functionalities allow looping through a group of tasks during playbook execution? (Choose two.)

Question18: What is the difference between an exception and an exclusion?
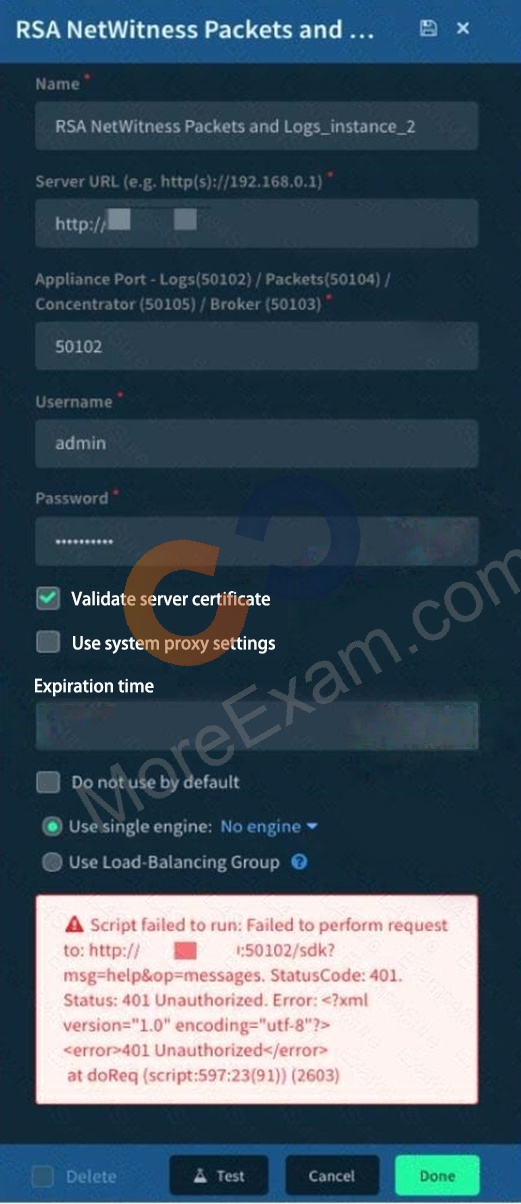
Question19: Given the integration configuration and error in the screenshot what is the cause of the problem?

Question20: How does an "inline" auto-extract task affect playbook execution?

Question21: In the DBotScore context field, which context key would differentiate between multiple entries for the same indicator in a multi-TIP environment?