EMT Practice Test

1. Question Content...


Question List

Question1: In acceptable use of Information Assets, which is the best practice?

Question2: Select the correct sequence for the information security risk assessment process in an ISMS.
To complete the sequence click on the blank section you want to complete so that it is highlighted in red, and then click on the applicable text from the options below. Alternatively, you may drag and drop the options to the appropriate blank

Question3: Match the correct responsibility with each participant of a second-party audit:

Question4: What is a repressive measure in case of a fire?
Question5: You receive an E-mail from some unknown person claiming to be representative of your bank and asking for your account number and password so that they can fix your account. Such an attempt of social engineering is called

Question6: Which department maintain's contacts with law enforcement authorities, regulatory bodies, information service providers and telecommunications service providers depending on the service required.

Question7: CMM stands for?

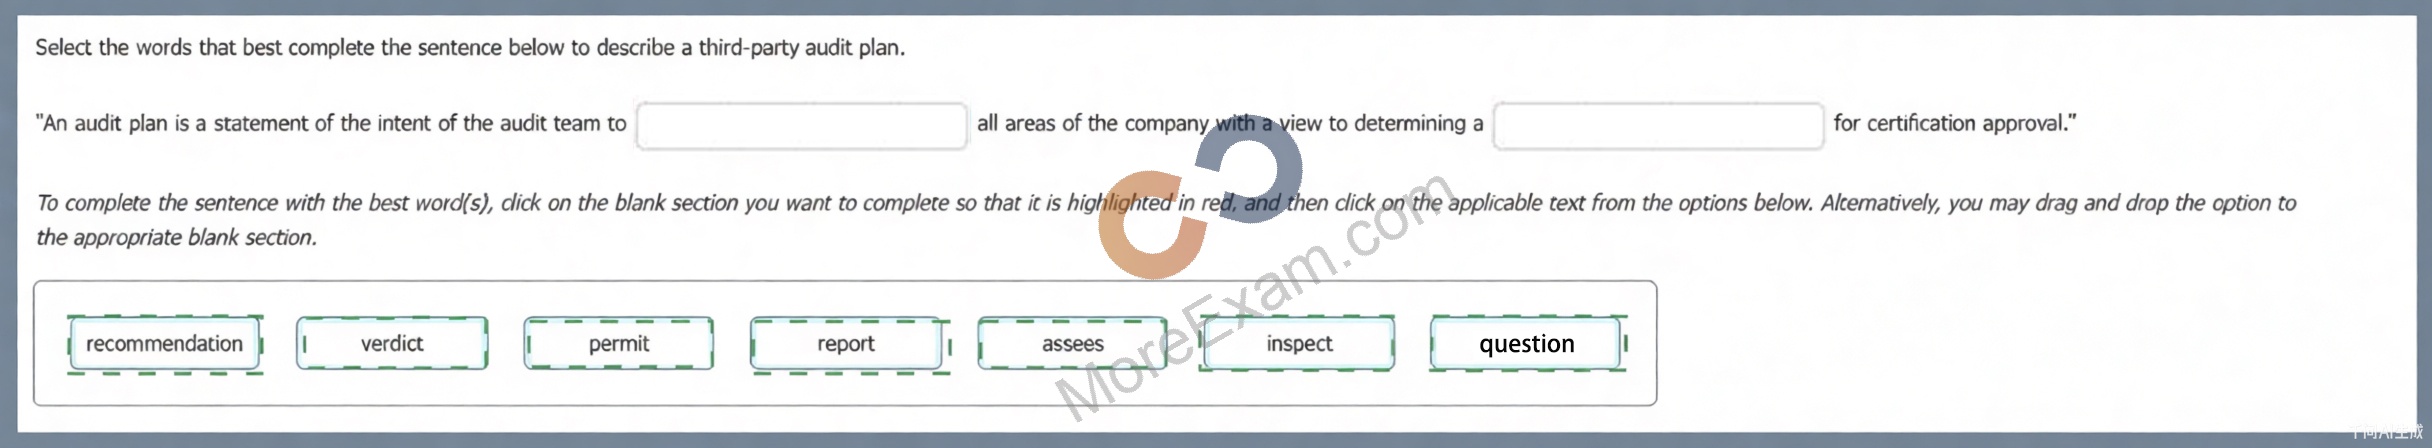
Question8: Select the words that best complete the sentence below to describe a third-party audit plan.
To complete the sentence with the best word(s), click on the blank section you want to complete so that it is highlighted in red, and then click on the applicable text from the options below. Alternatively, you may drag and drop the option to the appropriate blank section.

Question9: In what part of the process to grant access to a system does the user present a token?

Question10: Who is responsible for Initial asset allocation to the user/custodian of the assets?

Question11: What would be the reference for you to know who should have access to data/document?

Question12: Which of the following does an Asset Register contain? (Choose two)
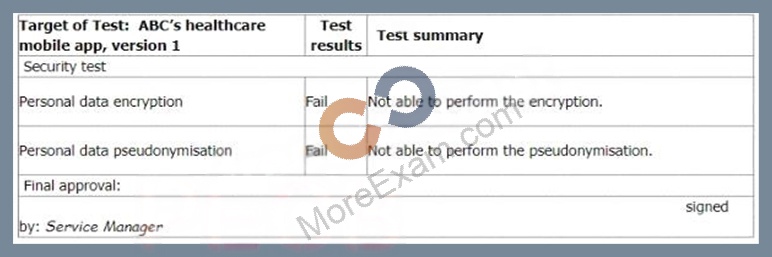
Question13: You are performing an ISMS audit at a residential nursing home (ABC) that provides healthcare services. The next step in your audit plan is to verify the information security of ABC's healthcare mobile app development, support, and lifecycle process.
During the audit, you learned the
organization outsourced the mobile app development to a professional software development company with CMMI Level 5, ITSM (ISO/IEC
20000-1), BCMS (ISO 22301) and ISMS (ISO/IEC 27001) certified.
The IT Manager presented the software security management procedure and summarised the process as following:
The mobile app development shall adopt "security-by-design" and "security-by-default" principles, as a minimum. The following security functions for personal data protection shall be available:
Access control.
Personal data encryption, i.e., Advanced Encryption Standard (AES) algorithm, key lengths: 256 bits; and Personal data pseudonymization.
Vulnerability checked and no security backdoor
You sample the latest Mobile App Test report, details as follows:

You ask the IT Manager why the organisation still uses the mobile app while personal data encryption and pseudonymization tests failed. Also, whether the Service Manager is authorised to approve the test.
The IT Manager explains the test results should be approved by him according to the software security management procedure.
The reason why the encryption and pseudonymisation functions failed is that these functions heavily slowed down the system and service performance. An extra 150% of resources are needed to cover this. The Service Manager agreed that access control is good enough and acceptable. That's why the Service Manager signed the approval.
You are preparing the audit findings. Select the correct option.

Question14: Which one of the following statements best describes the purpose of conducting a document review?

Question15: What controls can you do to protect sensitive data in your computer when you go out for lunch?

Question16: Four types of Data Classification (Choose two)

Question17: In the context of a management system audit, please identify the sequence of a typical process of collecting and verifying information. The first one has been done for you.

Question18: You are performing an ISMS audit at a residential nursing home railed ABC that provides healthcare services.
The next step in your audit plan is to verify the effectiveness of the continual improvement process. During the audit, you learned most of the residents' family members (90%) receive WeCare medical device promotional advertisements through email and SMS once a week via ABC's healthcare mobile app. All of them do not agree on the use of the collected personal data (or marketing or any other purposes than nursing and medical care on the signed service agreement with ABC. They have very strong reason to believe that ABC is leaking residents' and family members' personal information to a non-relevant third party and they have filed complaints.
The Service Manager says that all these complaints have been treated as nonconformities, and the corrective actions have been planned and implemented according to the Nonconformity and Corrective management procedure. The corrective action involved stopping working with WeCare the medical device manufacturer immediately and asking them to delete all personal data received as well as sending an apology email to all residents and their family members.
You are preparing the audit findings. Select one option of the correct finding.

Question19: There is a scheduled fire drill in your facility. What should you do?

Question20: Which one of the following options is the definition of the context of an organisation?

Question21: You are an experienced ISMS audit team leader, assisting an auditor in training to write their first audit report.
You want to check the auditor in training's understanding of terminology relating to the contents of an audit report and chose to do this by presenting the following examples.
For each example, you ask the auditor in training what the correct term is that describes the activity Match the activity to the description.

Question22: You are performing an ISMS audit at a European-based residential
nursing home called ABC that provides healthcare services. You find all nursing home residents wear an electronic wristband for monitoring their location, heartbeat, and blood pressure always. You learned that the electronic wristband automatically uploads all data to the artificial intelligence (AI) cloud server for healthcare monitoring and analysis by healthcare staff.
The next step in your audit plan is to verify that the information security policy and objectives have been established by top management.
During the audit, you found the following audit evidence.
Match the audit evidence to the corresponding requirement in ISO/IEC 27001:2022.

Question23: Auditors need to communicate effectively with auditees. Therefore, their personal behaviour is a key characteristic needed to ensure a successful audit. Below there are the characteristics and a brief related description. Match the characteristics to the descriptions.

Question24: Who is authorized to change the classification of a document?

Question25: Which of the following factors does NOT contribute to the value of data for an organisation?

Question26: What is social engineering?
Question27: As a new member of the IT department you have noticed that confidential information has been leaked several times. This may damage the reputation of the company. You have been asked to propose an organisational measure to protect laptop computers. What is the first step in a structured approach to come up with this measure?

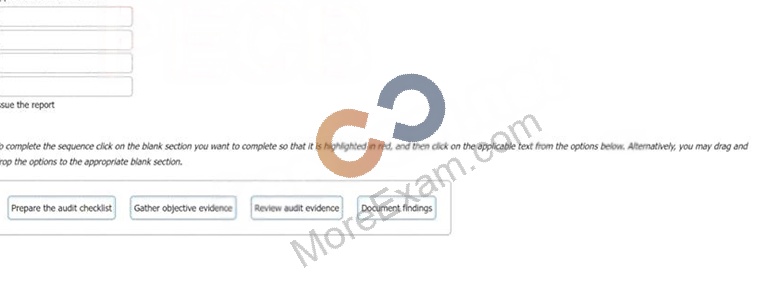
Question28: The following options are key actions involved in a first-party audit. Order the stages to show the sequence in which the actions should take place.

Question29: Your organisation is currently seeking ISO/IEC27001:2022 certification. You have just qualified as an Internal ISMS auditor and the ICT Manager wants to use your newly acquired knowledge to assist him with the design of an information security incident management process.
He identifies the following stages in his planned process and asks you to confirm which order they should appear in.

Question30: Often, people do not pick up their prints from a shared printer. How can this affect the confidentiality of information?

Question31: You receive the following mail from the IT support team: Dear User,Starting next week, we will be deleting all inactive email accounts in order to create spaceshare the below details in order to continue using your account. In case of no response, Name:
Email ID:
Password:
DOB:
Kindly contact the webmail team for any further support. Thanks for your attention.
Which of the following is the best response?

Question32: After a devastating office fire, all staff are moved to other branches of the company. At what moment in the incident management process is this measure effectuated?

Question33: You are an ISMS audit team leader assigned by your certification body to carry out a follow-up audit of a Data Centre client.
According to ISO 19011:2018, the purpose of a follow-up audit is to verify which one of the following?

Question34: An employee caught with offense of abusing the internet, such as P2P file sharing or video/audio streaming, will not receive a warning for committing such act but will directly receive an IR.

Question35: What type of measure involves the stopping of possible consequences of security incidents?

Question36: During discussions with the individual(s) managing the audit programme of a certification body, the Management System Representative of the client organisation asks for a specific auditor for the certification audit. Select two of the following options for how the individual(s) managing the audit programme should respond.

Question37: Does the security have the right to ask you to display your ID badges and check your bags?

Question38: Phishing is what type of Information Security Incident?

Question39: Please match the following situations to the type of audit required.

Question40: Which of the following is a preventive security measure?

Question41: What is the worst possible action that an employee may receive for sharing his or her password or access with others?

Question42: What is the difference between a restricted and confidential document?

Question43: Changes on project-managed applications or database should undergo the change control process as documented.

Question44: Select the words that best complete the sentence:

Question45: Which of the following does a lack of adequate security controls represent?

Question46: Select the words that best complete the sentence:
To complete the sentence with the word(s) click on the blank section you want to complete so that it is highlighted in red, and then click on the application text from the options below. Alternatively, you may drag and drop the option to the appropriate blank section.

Question47: A planning process that introduced the concept of planning as a cycle that forms the basis for continuous improvement is called:

Question48: You are an experienced ISMS audit team leader conducting a third-party surveillance visit.
You notice that although the auditee is claiming conformity with ISO/IEC 27001:2022 they are still referring to Improvement as clause 10.2 (as it was in the 2013 edition) when this is now clause 10.1 in the 2022 edition. You have confirmed they are meeting all of the 2022 requirements set out in the standard.
Select one option of the action you should take.

Question49: How is the purpose of information security policy best described?

Question50: Select the words that best complete the sentence:

Question51: The following are purposes of Information Security, except:

Question52: Which is not a requirement of HR prior to hiring?

Question53: There was a fire in a branch of the company Midwest Insurance. The fire department quickly arrived at the scene and could extinguish the fire before it spread and burned down the entire premises. The server, however, was destroyed in the fire. The backup tapes kept in another room had melted and many other documents were lost for good.
What is an example of the indirect damage caused by this fire?

Question54: Which of the following is not a type of Information Security attack?

Question55: What is the security management term for establishing whether someone's identity is correct?

Question56: Which is the glue that ties the triad together

Question57: Stages of Information