EMT Practice Test

1. Question Content...


Question List

Question1: Which one of the following options is the definition of an interested party?

Question2: Select the words that best complete the sentence:

Question3: Which is the glue that ties the triad together

Question4: Which one of the following options is the definition of an interested party?
Question5: Below is Purpose of "Integrity", which is one of the Basic Components of Information Security

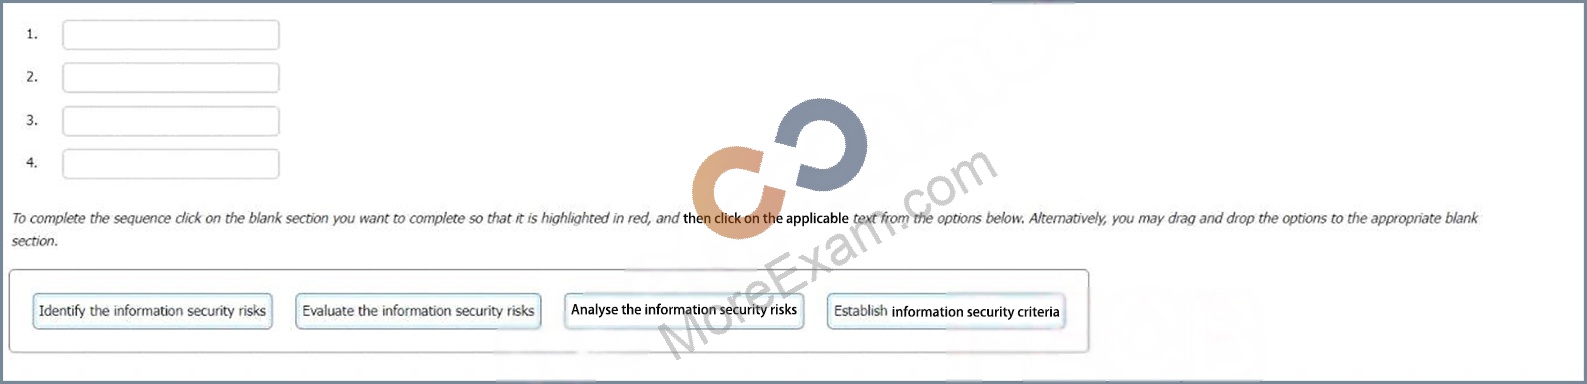
Question6: Select the correct sequence for the information security risk assessment process in an ISMS.
To complete the sequence click on the blank section you want to complete so that it is highlighted in red, and then click on the applicable text from the options below. Alternatively, you may drag and drop the options to the appropriate blank

Question7:

Question8: As the ISMS audit team leader, you are conducting a second-party audit of an international logistics company on behalf of an online retailer. During the audit, one of your team members reports a nonconformity relating to control 5.18 (Access rights) of Appendix A of ISO/IEC 27001:2022. She found evidence that removing the server access protocols of 20 people who left in the last 3 months took up to 1 week whereas the policy required removing access within 24 hours of their departure.
Complete the sentence with the best word(s), dick on the blank section you want to complete so that it is highlighted in red, and then click on the applicable text from the options below. Alternatively, you may drag and drop the option to the appropriate blank section.

Question9:

Question10: Stages of Information

Question11: -------------------------is an asset like other important business assets has value to an organization and consequently needs to be protected.

Question12: In acceptable use of Information Assets, which is the best practice?

Question13: In the event of an Information security incident, system users' roles and responsibilities are to be observed, except:

Question14: Which one of the following options best describes the main purpose of a Stage 2 third-party audit?

Question15:

Question16: Which one of the following conclusions in the audit report is not required by the certification body when deciding to grant certification?

Question17:

Question18:

Question19:

Question20: Which one of the following options is the definition of an interested party?

Question21:

Question22: Select the word that best completes the sentence:

Question23: You are an experienced ISMS audit team leader conducting a third-party surveillance visit.
You notice that although the auditee is claiming conformity with ISO/IEC 27001:2022 they are still referring to Improvement as clause 10.2 (as it was in the 2013 edition) when this is now clause 10.1 in the 2022 edition. You have confirmed they are meeting all of the 2022 requirements set out in the standard.
Select one option of the action you should take.

Question24: A key audit process is the way auditors gather information and determine the findings' characteristics. Put the actions listed in the correct order to complete this process. The last one has been done for you.

Question25: During discussions with the individual(s) managing the audit programme of a certification body, the Management System Representative of the client organisation asks for a specific auditor for the certification audit. Select two of the following options for how the individual(s) managing the audit programme should respond.

Question26: You are an experienced ISMS audit team leader. An auditor in training has approached you to ask you to clarify the different types of audits she may be required to undertake.
Match the following audit types to the descriptions.
To complete the table click on the blank section you want to complete so that It is highlighted In fed, and then click on the applicable text from the options below. Alternatively, you may drag and drop each option to the appropriate blank section.

Question27: Select the words that best complete the sentence below to describe a third-party audit plan.
To complete the sentence with the best word(s), click on the blank section you want to complete so that it is highlighted in red, and then click on the applicable text from the options below. Alternatively, you may drag and drop the option to the appropriate blank section.

Question28: Which one of the following options is the definition of the context of an organisation?

Question29: Select the words that best complete the sentence:
To complete the sentence with the word(s) click on the blank section you want to complete so that it is highlighted in red, and then click on the application text from the options below. Alternatively, you may drag and drop the option to the appropriate blank section.

Question30:

Question31: Which one of the following options is the definition of an interested party?

Question32: The following are definitions of Information, except:

Question33: You have a hard copy of a customer design document that you want to dispose off. What would you do

Question34: Which one of the following options is the definition of an interested party?

Question35:

Question36:

Question37:

Question38: Select the words that best complete the sentence below to describe audit resources:

Question39: Which one of the following options is the definition of an interested party?

Question40: Which one of the following options is the definition of an interested party?

Question41: Which one of the following options is the definition of an interested party?

Question42: Which one of the following options is the definition of an interested party?

Question43:

Question44: Which one of the following options is the definition of an interested party?

Question45:

Question46:

Question47:

Question48:

Question49:

Question50:

Question51: Implement plan on a test basis - this comes under which section of PDCA

Question52: The audit team leader prepares the audit plan for an initial certification stage 2 audit to ISO/IEC 27001:2022.
Which one of the following statements is true?

Question53: You are performing an ISMS audit at a European-based residential
nursing home called ABC that provides healthcare services. You find all nursing home residents wear an electronic wristband for monitoring their location, heartbeat, and blood pressure always. You learned that the electronic wristband automatically uploads all data to the artificial intelligence (AI) cloud server for healthcare monitoring and analysis by healthcare staff.
The next step in your audit plan is to verify that the information security policy and objectives have been established by top management.
During the audit, you found the following audit evidence.
Match the audit evidence to the corresponding requirement in ISO/IEC 27001:2022.

Question54: You are an experienced ISMS audit team leader providing instruction to a class of auditors in training. The subject of today's lesson is the management of information security risk in accordance with the requirements of ISO/IEC 27001:2022.
You provide the class with a series of activities. You then ask the class to sort these activities into the order in which they appear in the standard.
What is the correct sequence they should report back to you?

Question55: Which two of the following are examples of audit methods that 'do' involve human interaction?

Question56: Which one option best describes the purpose of retaining documented information related to the Information Security Management System (ISMS) of an organisation?

Question57:

Question58: