EMT Practice Test

1. Question Content...


Question List

Question1: Cabling Security is associated with Power, telecommunication and network cabling carrying information are protected from interception and damage.

Question2: What type of measure involves the stopping of possible consequences of security incidents?

Question3: Someone from a large tech company calls you on behalf of your company to check the health of your PC, and therefore needs your user-id and password. What type of threat is this?

Question4: A decent visitor is roaming around without visitor's ID. As an employee you should do the following, except:

Question5:

Question6: As a new member of the IT department you have noticed that confidential information has been leaked several times. This may damage the reputation of the company. You have been asked to propose an organisational measure to protect laptop computers. What is the first step in a structured approach to come up with this measure?

Question7: Information or data that are classified as ______ do not require labeling.

Question8: Your organisation is currently seeking ISO/IEC27001:2022 certification. You have just qualified as an Internal ISMS auditor and the ICT Manager wants to use your newly acquired knowledge to assist him with the design of an information security incident management process.
He identifies the following stages in his planned process and asks you to confirm which order they should appear in.

Question9: What is the relationship between data and information?

Question10: You are performing an ISMS audit at a residential nursing home (ABC) that provides healthcare services. The next step in your audit plan is to verify the information security of ABC's healthcare mobile app development, support, and lifecycle process.
During the audit, you learned the
organization outsourced the mobile app development to a professional software development company with CMMI Level 5, ITSM (ISO/IEC
20000-1), BCMS (ISO 22301) and ISMS (ISO/IEC 27001) certified.
The IT Manager presented the software security management procedure and summarised the process as following:
The mobile app development shall adopt "security-by-design" and "security-by-default" principles, as a minimum. The following security functions for personal data protection shall be available:
Access control.
Personal data encryption, i.e., Advanced Encryption Standard (AES) algorithm, key lengths: 256 bits; and Personal data pseudonymization.
Vulnerability checked and no security backdoor
You sample the latest Mobile App Test report, details as follows:

You ask the IT Manager why the organisation still uses the mobile app while personal data encryption and pseudonymisation tests failed. Also, whether the Service Manager is authorised to approve the test.
The IT Manager explains the test results should be approved by him according to the software security management procedure.
The reason why the encryption and pseudonymisation functions failed is that these functions heavily slowed down the system and service performance. An extra 150% of resources are needed to cover this. The Service Manager agreed that access control is good enough and acceptable. That's why the Service Manager signed the approval.
You are preparing the audit findings. Select the correct option.

Question11: During discussions with the individual(s) managing the audit programme of a certification body, the Management System Representative of the client organisation asks for a specific auditor for the certification audit. Select two of the following options for how the individual(s) managing the audit programme should respond.

Question12: What is a repressive measure in case of a fire?

Question13: Which of the following statements are correct for Clean Desk Policy?

Question14: Implement plan on a test basis - this comes under which section of PDCA

Question15: Which of the following is an information security management system standard published by the International Organization for Standardization?

Question16: Below is Purpose of "Integrity", which is one of the Basic Components of Information Security

Question17: Which one of the following options is the definition of an interested party?

Question18: A scenario wherein the city or location where the building(s) reside is / are not accessible.

Question19: What is the goal of classification of information?

Question20: Which two of the following statements are true?

Question21: What is the security management term for establishing whether someone's identity is correct?

Question22: Which threat could occur if no physical measures are taken?

Question23: What is an example of a human threat?
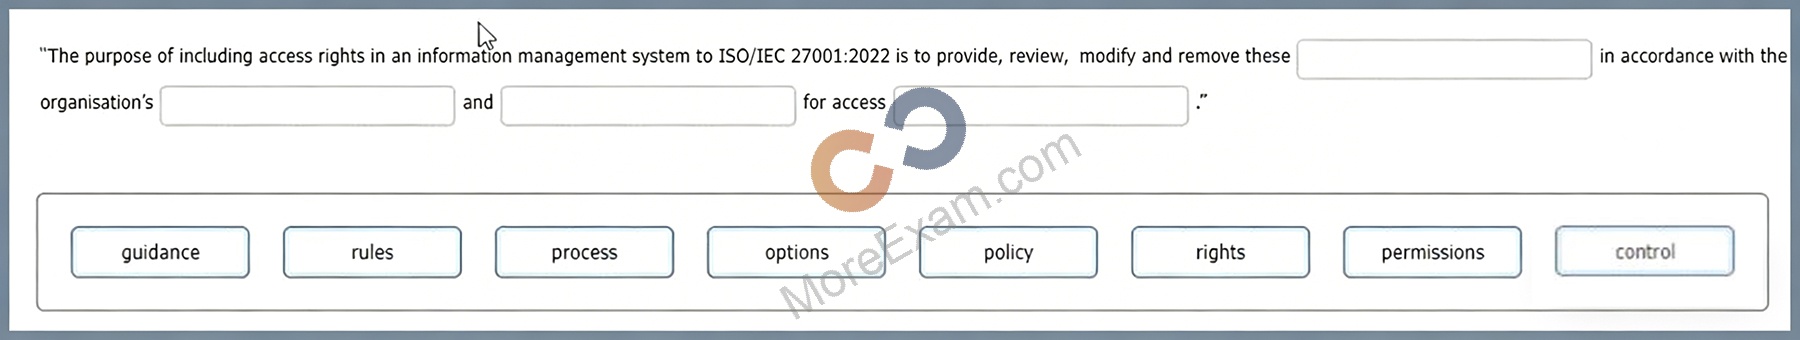
Question24: As the ISMS audit team leader, you are conducting a second-party audit of an international logistics company on behalf of an online retailer. During the audit, one of your team members reports a nonconformity relating to control 5.18 (Access rights) of Appendix A of ISO/IEC 27001:2022. She found evidence that removing the server access protocols of 20 people who left in the last 3 months took up to 1 week whereas the policy required removing access within 24 hours of their departure.
Complete the sentence with the best word(s), dick on the blank section you want to complete so that it is highlighted in red, and then click on the applicable text from the options below. Alternatively, you may drag and drop the option to the appropriate blank section.

Question25: What is a definition of compliance?

Question26: The audit team leader prepares the audit plan for an initial certification stage 2 audit to ISO/IEC 27001:2022.
Which one of the following statements is true?

Question27: An administration office is going to determine the dangers to which it is exposed.
What do we call a possible event that can have a disruptive effect on the reliability of information?

Question28: What is the name of the system that guarantees the coherence of information security in the organization?

Question29: Who is authorized to change the classification of a document?

Question30: What type of system ensures a coherent Information Security organisation?

Question31: What is a repressive measure in case of a fire?

Question32: Which measure is a preventive measure?

Question33: A property of Information that has the ability to prove occurrence of a claimed event.

Question34: Auditors need to communicate effectively with auditees. Therefore, their personal behaviour is a key characteristic needed to ensure a successful audit. Below there are the characteristics and a brief related description. Match the characteristics to the descriptions.

Question35: Match the correct responsibility with each participant of a second-party audit:

Question36: How is the purpose of information security policy best described?

Question37: CEO sends a mail giving his views on the status of the company and the company's future strategy and the CEO's vision and the employee's part in it. The mail should be classified as

Question38: What would be the reference for you to know who should have access to data/document?

Question39: There was a fire in a branch of the company Midwest Insurance. The fire department quickly arrived at the scene and could extinguish the fire before it spread and burned down the entire premises. The server, however, was destroyed in the fire. The backup tapes kept in another room had melted and many other documents were lost for good.
What is an example of the indirect damage caused by this fire?

Question40: A well-executed risk analysis provides a great deal of useful information. A risk analysis has four main objectives.
What is not one of the four main objectives of a risk analysis?

Question41: The following are purposes of Information Security, except:

Question42: In acceptable use of Information Assets, which is the best practice?

Question43: All are prohibited in acceptable use of information assets, except:

Question44: Information Security is a matter of building and maintaining ________ .

Question45: Which one of the following statements best describes the purpose of conducting a document review?

Question46: Please match the roles to the following descriptions:

To complete the table click on the blank section you want to complete so that it is highlighted in red, and then click on the applicable test from the options below. Alternatively, you may drag and drop each option to the appropriate blank section.

Question47: Four types of Data Classification (Choose two)

Question48: Information has a number of reliability aspects. Reliability is constantly being threatened. Examples of threats are: a cable becomes loose, someone alters information by accident, data is used privately or is falsified.
Which of these examples is a threat to integrity?

Question49: A couple of years ago you started your company which has now grown from 1 to 20 employees. Your company's information is worth more and more and gone are the days when you could keep control yourself.
You are aware that you have to take measures, but what should they be? You hire a consultant who advises you to start with a qualitative risk analysis.
What is a qualitative risk analysis?

Question50: You receive an E-mail from some unknown person claiming to be representative of your bank and asking for your account number and password so that they can fix your account. Such an attempt of social engineering is called

Question51: The audit lifecycle describes the ISO 19011 process for conducting an individual audit. Drag and drop the steps of the audit lifecycle into the correct sequence.

Question52: Integrity of data means

Question53: -------------------------is an asset like other important business assets has value to an organization and consequently needs to be protected.

Question54: What is the standard definition of ISMS?

Question55: An employee caught with offense of abusing the internet, such as P2P file sharing or video/audio streaming, will not receive a warning for committing such act but will directly receive an IR.

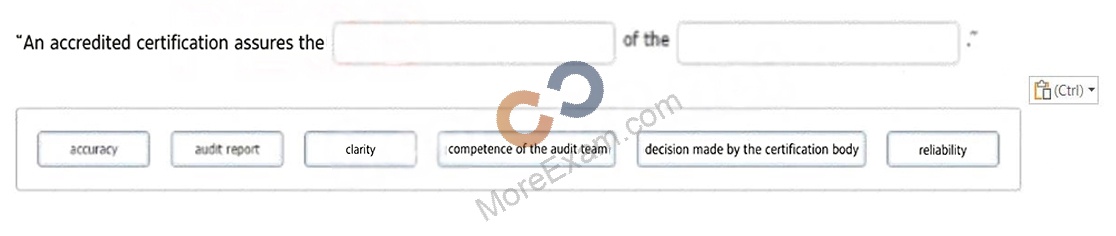
Question56: Select the words that best complete the sentence:
Question57: You are performing an ISMS audit at a residential nursing home railed ABC that provides healthcare services.
The next step in your audit plan is to verify the effectiveness of the continual improvement process. During the audit, you learned most of the residents' family members (90%) receive WeCare medical device promotional advertisements through email and SMS once a week via ABC's healthcare mobile app. All of them do not agree on the use of the collected personal data (or marketing or any other purposes than nursing and medical care on the signed service agreement with ABC. They have very strong reason to believe that ABC is leaking residents' and family members' personal information to a non-relevant third party and they have filed complaints.
The Service Manager says that all these complaints have been treated as nonconformities, and the corrective actions have been planned and implemented according to the Nonconformity and Corrective management procedure. The corrective action involved stopping working with WeCare the medical device manufacturer immediately and asking them to delete all personal data received as well as sending an apology email to all residents and their family members.
You are preparing the audit findings. Select one option of the correct finding.

Question58: You see a blue color sticker on certain physical assets. What does this signify?

Question59: A hacker gains access to a webserver and can view a file on the server containing credit card numbers.
Which of the Confidentiality, Integrity, Availability (CIA) principles of the credit card file are violated?

Question60: Phishing is what type of Information Security Incident?
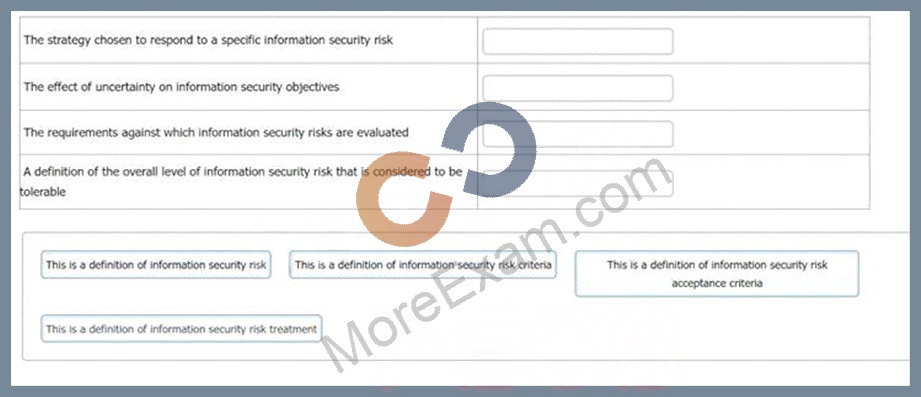
Question61: You have just completed a scheduled information security audit of your organisation when the IT Manager approaches you and asks for your assistance in the revision of the company's risk management process.
He is attempting to update the current documentation to make it easier for other managers to understand, however, it is clear from your discussion he is confusing several key terms.
You ask him to match each of the descriptions with the appropriate risk term. What should the correct answers be?

Question62: You receive the following mail from the IT support team: Dear User,Starting next week, we will be deleting all inactive email accounts in order to create spaceshare the below details in order to continue using your account. In case of no response, Name:
Email ID:
Password:
DOB:
Kindly contact the webmail team for any further support. Thanks for your attention.
Which of the following is the best response?

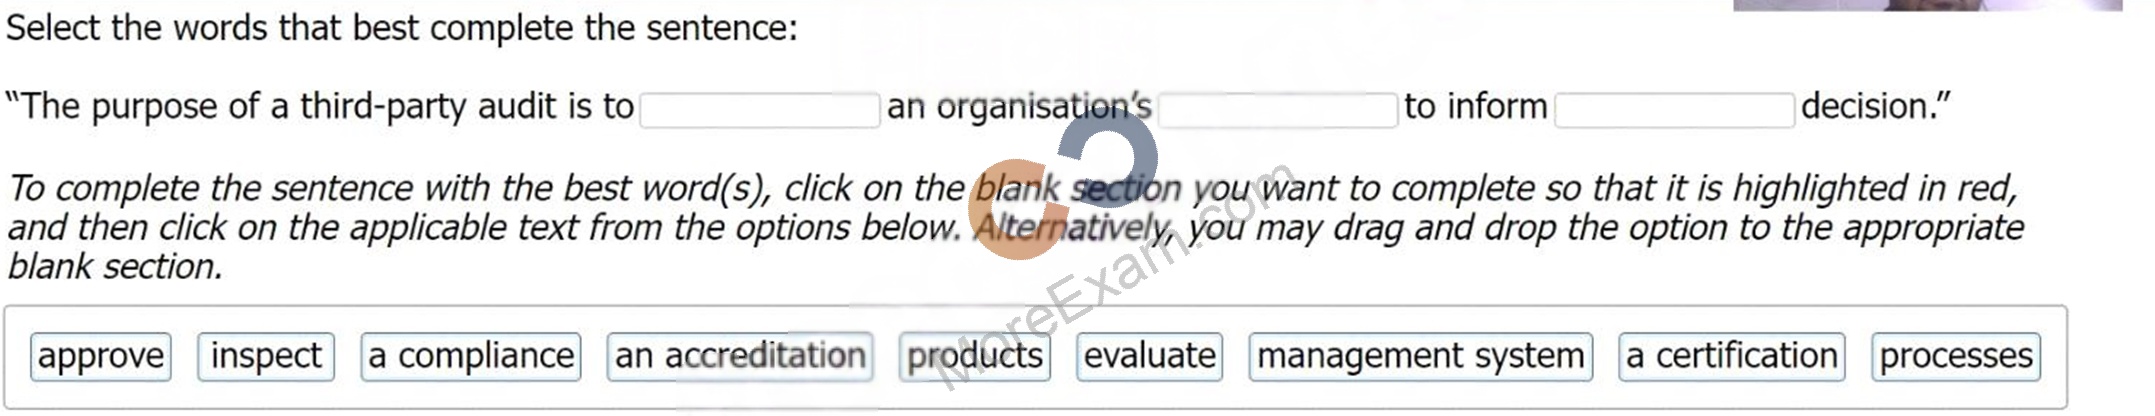
Question63: Select the words that best complete the sentence:
To complete the sentence with the word(s) click on the blank section you want to complete so that it is highlighted in red, and then click on the application text from the options below. Alternatively, you may drag and drop the option to the appropriate blank section.